Best alternative to Pentest Agencies, meet Jikida.
A traditional pentest agency runs one manual engagement, months apart, for a four-figure fee. Jikida runs the pentest on a schedule, grades it, and adds repo scanning, a firewall and uptime, at developer pricing.
Why teams pick Jikida over Pentest Agencies.
A manual pentest agency has real value. A skilled human tester finds logic flaws and chained exploits that no automated pass will catch, and for a compliance audit or a high-risk launch that human review is worth paying for. If you need a signed report from a named firm once a year, an agency is the right tool.
The gap most teams hit is cadence and cost. An agency engagement is a four-figure line item, it takes weeks to scope and schedule, and the report is a snapshot of one day. Your code ships every week, so by the time the next audit runs, the app under test has changed many times. Jikida runs the pentest on a schedule instead of once a year, grades the result, and gives a fix for each finding, so the gap between audits is covered.
People searching for a cheaper pentest, or continuous pentesting for a small team, usually want the coverage without the retainer. Jikida tests the running app, scans the repo for secrets and vulnerable dependencies, blocks live attacks with a managed WAF, and watches uptime, all from one account with a free tier that needs no card.
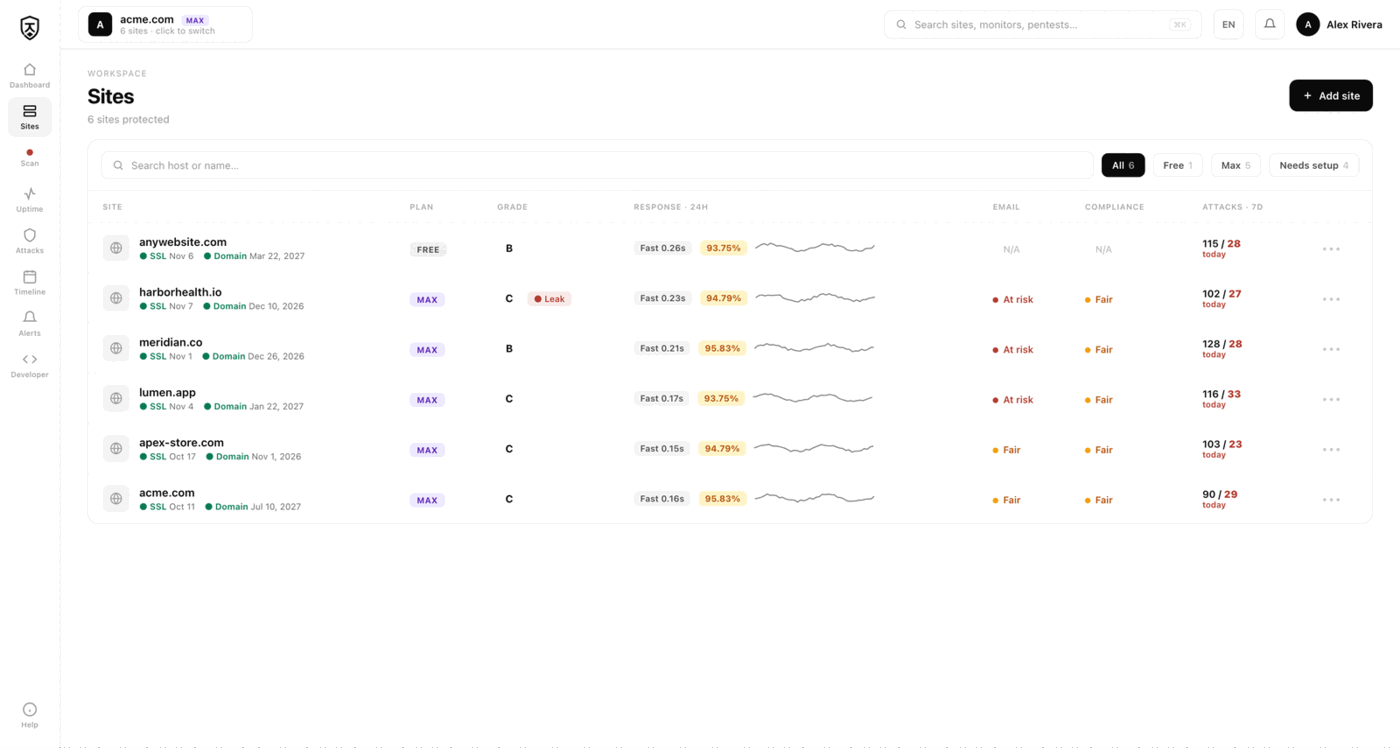
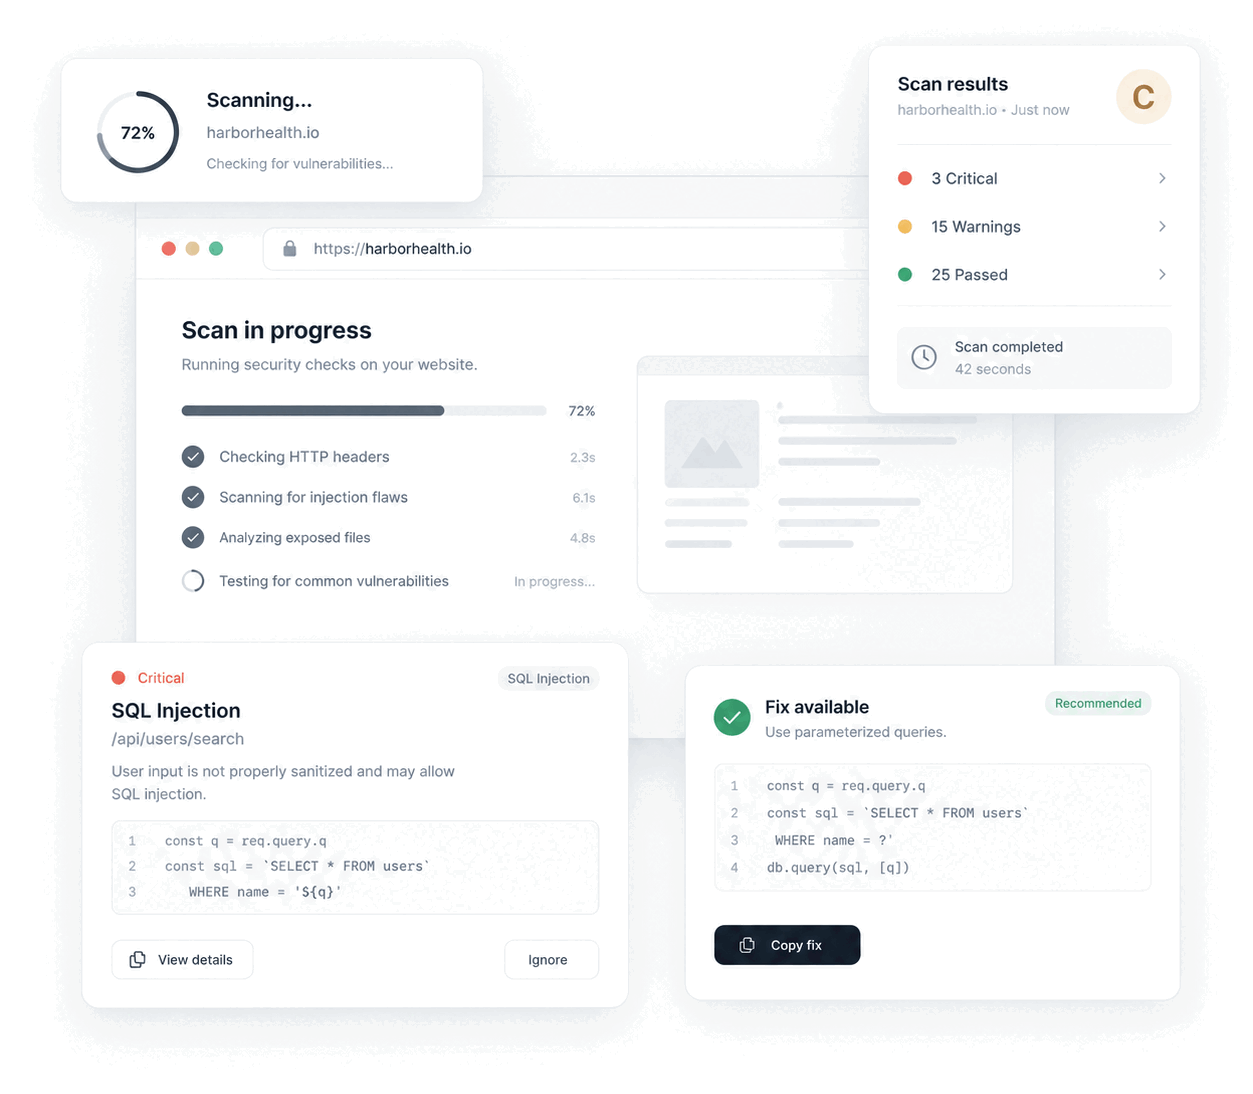
Switching from Pentest Agencies to Jikida.
The honest split is this: use an agency for the deep, human, point-in-time audit you need for compliance, and use Jikida for the continuous testing that keeps the weeks in between covered. The two are not the same job. A live-app pentest from Jikida checks security headers, TLS, exposed .env, .git and laravel.log files, client secrets, open ports, admin panels, CORS, reflected XSS, subdomain takeover, GraphQL introspection and HTTP methods, with a fix for each finding and a grade you can track over time.
Around the pentest, Jikida covers ground an agency report does not. The repo scan reads your code for committed secrets and vulnerable dependencies via OSV plus a malicious-package feed. A managed WAF blocks the live attacks the scan finds, and monitoring watches uptime, SSL and domain expiry with a call-style phone alarm. The CLI (npx @jikida/scan) outputs SARIF with --fail-on so a scan can gate CI, and MCP tools bring scans into Claude Code, Cursor and Windsurf.
Nothing to migrate, and nothing to schedule. Point Jikida at your live URL and repo, and the scheduled pentest, code scan, WAF and uptime alerts turn on in minutes. There is no scoping call and no minimum spend. Install is one line, and it fails open, so a Jikida outage never blocks your traffic. Keep the agency for the annual audit if you need the signed report, and let Jikida cover the other fifty-one weeks. The free tier needs no card.
Compare Jikida with the rest.
How to switch from Pentest Agencies without a monitoring gap.
Migrating off Pentest Agencies is a five-minute job, not a project. You keep Pentest Agencies live while you set Jikida up, move your sites and alerts across, switch on the WAF and pentest Pentest Agencies never offered, and only then cancel. Here is the exact order.
-
01
Keep Pentest Agencies running while you set up
No rip-and-replace. Create a free Jikida account and add your sites there first, and Pentest Agencies stays live the whole time, so there is never a monitoring gap during the move.
-
02
Add your sites and endpoints
Point Jikida at the same URLs, domains and API endpoints you watch in Pentest Agencies. Uptime checks, SSL and domain-expiry monitoring and a public status page turn on the moment a site is added: no agent to install, no DNS change.
-
03
Wire up the alerts you already use
Connect email, Slack, Discord, Telegram or a signed webhook, and install the Jikida Alerts phone app. The call-style Alarm level rings through silent mode and Do Not Disturb for the 3am outage you cannot sleep through, something Pentest Agencies cannot do.
-
04
Turn on the security Pentest Agencies does not have
This is the real upgrade: a managed WAF in one SDK line, a scheduled pentest that grades your site A–F, repo and secret scanning, and active deception, all in the same account, at no extra vendor. Monitoring and security stop being two bills.
-
05
Run both for a cycle, then cancel Pentest Agencies
Watch the two side by side for a billing cycle. Once you trust the Jikida alerts and grades, cancel Pentest Agencies and consolidate. Most teams find they were paying for uptime and still had no security layer at all.
Frequently asked questions.
Everything people ask before they switch from Pentest Agencies. Still unsure? We are one message away.
For the continuous testing between audits, yes. Jikida runs a live-app pentest on a schedule, grades it, and gives a fix per finding. For a signed, point-in-time report from a named firm for compliance, keep an agency for that audit and let Jikida cover the weeks in between, when your code keeps changing.
A traditional agency engagement is usually a four-figure fee per test, scheduled weeks ahead. Jikida is priced for individual developers and small teams, and the free tier needs no card. You get a scheduled live-app pentest, repo scanning, a managed WAF and uptime monitoring in one account. See /features.
It finds a different set. A human is better at business-logic and chained exploits. Automated testing is better at running often and catching the exposed files, weak headers, open ports, injection and misconfiguration that appear between audits. Jikida runs the automated pass on a schedule, so the common issues never sit unchecked for a year.
Minutes, not weeks. There is no scoping call and no contract. Point Jikida at your live URL and repo, and the scheduled pentest and scans begin. An agency engagement usually needs scoping, scheduling and a statement of work before any testing starts.
Yes, no card needed. Free covers one live-app pentest, one repo scan, uptime monitoring and a basic managed WAF. Paid plans add scheduled deep pentests, monthly repo scans, the full WAF and unlimited MCP scans, still far below a per-engagement agency fee.
One platform · One install
Pentest, scan and protect from one account.
A live-app pentest, repo and secret scanning, a managed firewall and monitoring — free to start, no card. Plans from $15/mo.