Best alternative to Pentest-Tools.com, meet Jikida.
Pentest-Tools.com gives you a large toolbox of individual scanners you run per target, one at a time. Jikida runs the pentest for you on a schedule, grades it with a fix per finding, then adds a repo scan, a managed WAF and uptime monitoring in one developer-priced account.
Why teams pick Jikida over Pentest-Tools.com.
Pentest-Tools.com is a good online toolbox. It gives you many individual scanners in one place, a port scanner, a website vulnerability scanner, subdomain and CMS checks, and more. You pick a tool, point it at a target, and read the report. For a security tester who wants a broad set of hosted scanners without installing them, it does the job well.
The gap developers hit is that a toolbox is a set of one-off runs. You choose the tool, start the scan, and check back later. It does not watch your code, block a live attack, or tell you the site is down at 3am. Jikida is built the other way around. You connect a site once, and it runs the pentest on a schedule, grades the result, and gives a fix for each finding. Then it adds the parts a scanner toolbox does not have.
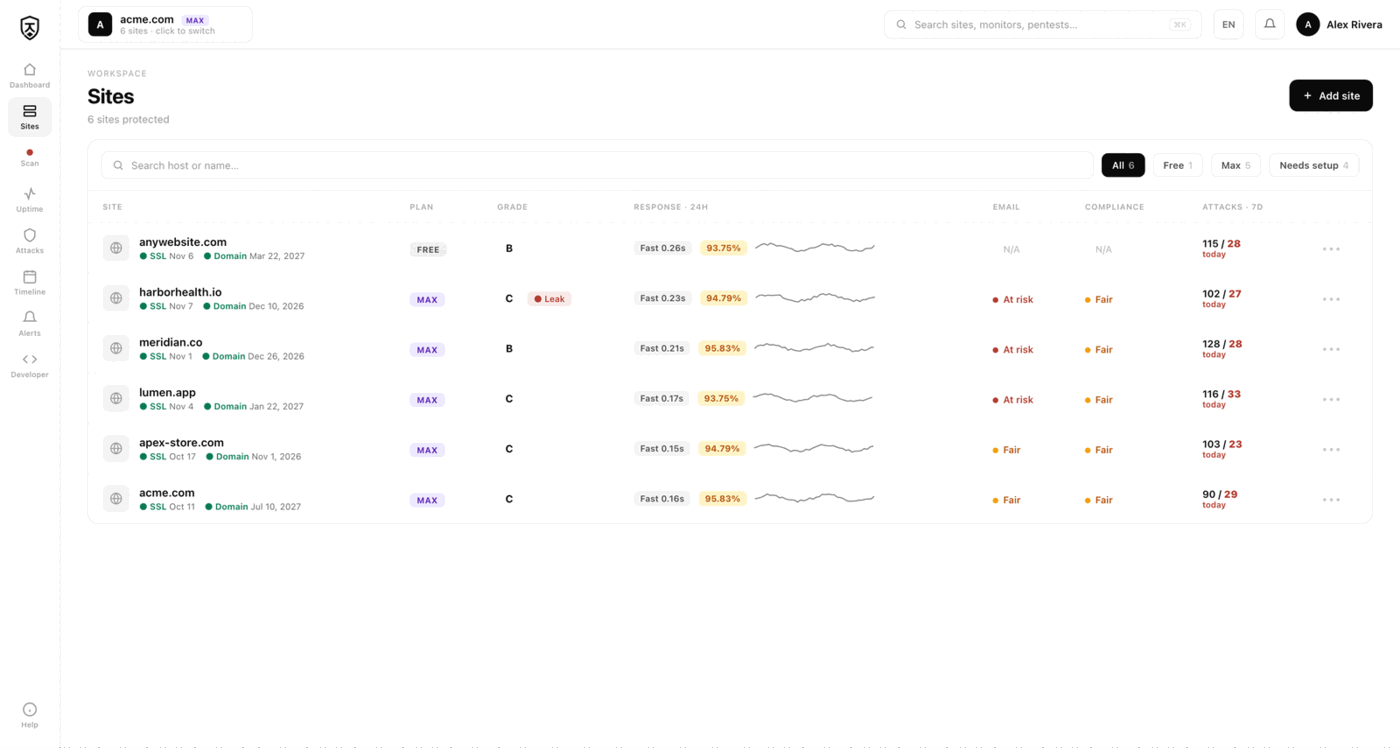
People searching for a Pentest-Tools.com alternative for solo developers, or a cheaper way to run DAST for indie devs, usually want less manual work and more coverage. Jikida pentests the running app, scans the repo for secrets and vulnerable dependencies, blocks attacks with a managed WAF, and watches uptime, all from one account with a free tier that needs no card.
Switching from Pentest-Tools.com to Jikida.
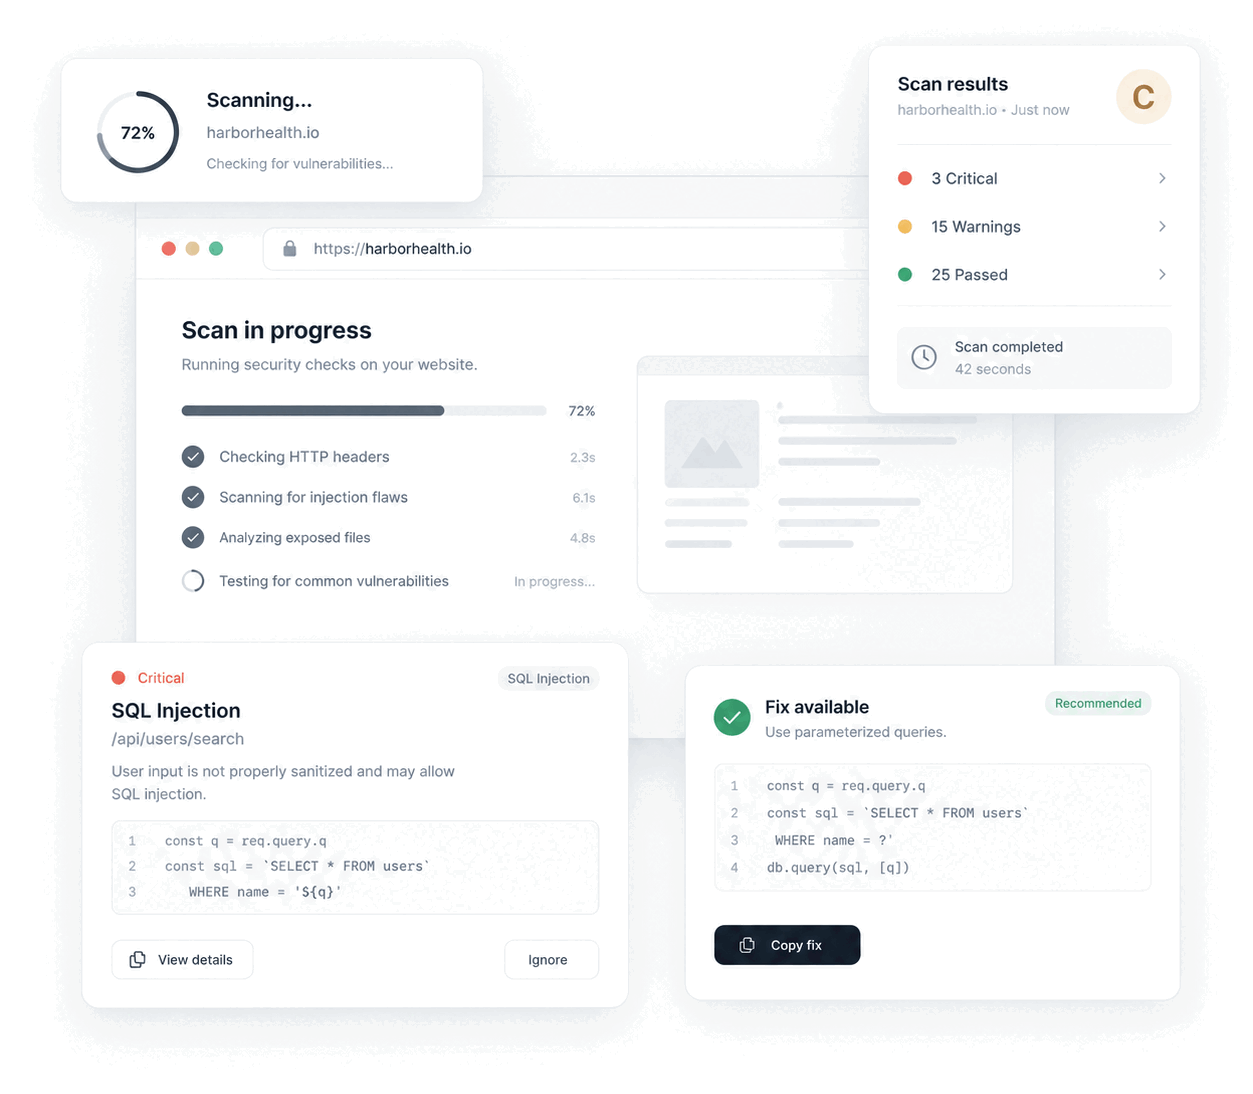
A scanner toolbox and a security platform solve different problems. Pentest-Tools.com is strong when a tester wants to run a specific scanner against a specific target on demand. Jikida is strong when a developer wants the whole app watched without running each tool by hand. The live-app pentest checks security headers, TLS, exposed .env, .git and laravel.log files, client secrets, open ports, admin panels, CORS, reflected XSS, subdomain takeover, GraphQL introspection and HTTP methods. Each finding comes with a fix, and the whole result is graded so you know where you stand at a glance.
Around the pentest, Jikida covers ground a scanner toolbox does not. The repo scan reads your code for committed secrets, dangerous patterns and vulnerable dependencies via OSV plus a malicious-package feed. A managed WAF blocks the live attacks the scan finds, and monitoring watches uptime, SSL and domain expiry with a call-style phone alarm. MCP tools bring scans into Claude Code, Cursor and Windsurf, and the CLI (npx @jikida/scan) outputs SARIF with --fail-on so a scan can gate CI.
Nothing to migrate. If you already use Pentest-Tools.com for one-off manual scans, keep it for that. Point Jikida at the same live URL and repo, and it runs the scheduled pentest, the code scan, the WAF and the uptime alerts beside it. Install is one line. It fails open, so a Jikida outage never blocks your traffic. The free tier needs no card and includes one pentest and one repo scan to try it.
Compare Jikida with the rest.
How to switch from Pentest-Tools.com without a monitoring gap.
Migrating off Pentest-Tools.com is a five-minute job, not a project. You keep Pentest-Tools.com live while you set Jikida up, move your sites and alerts across, switch on the WAF and pentest Pentest-Tools.com never offered, and only then cancel. Here is the exact order.
-
01
Keep Pentest-Tools.com running while you set up
No rip-and-replace. Create a free Jikida account and add your sites there first, and Pentest-Tools.com stays live the whole time, so there is never a monitoring gap during the move.
-
02
Add your sites and endpoints
Point Jikida at the same URLs, domains and API endpoints you watch in Pentest-Tools.com. Uptime checks, SSL and domain-expiry monitoring and a public status page turn on the moment a site is added: no agent to install, no DNS change.
-
03
Wire up the alerts you already use
Connect email, Slack, Discord, Telegram or a signed webhook, and install the Jikida Alerts phone app. The call-style Alarm level rings through silent mode and Do Not Disturb for the 3am outage you cannot sleep through, something Pentest-Tools.com cannot do.
-
04
Turn on the security Pentest-Tools.com does not have
This is the real upgrade: a managed WAF in one SDK line, a scheduled pentest that grades your site A–F, repo and secret scanning, and active deception, all in the same account, at no extra vendor. Monitoring and security stop being two bills.
-
05
Run both for a cycle, then cancel Pentest-Tools.com
Watch the two side by side for a billing cycle. Once you trust the Jikida alerts and grades, cancel Pentest-Tools.com and consolidate. Most teams find they were paying for uptime and still had no security layer at all.
Frequently asked questions.
Everything people ask before they switch from Pentest-Tools.com. Still unsure? We are one message away.
For developers who want the pentest run for them on a schedule, yes. Pentest-Tools.com gives you individual scanners to run per target by hand. Jikida connects to a site once, runs the pentest automatically, grades it with a fix per finding, and adds a repo scan, a managed WAF and uptime monitoring in one account.
Jikida is priced for individual developers and small teams, and the free tier needs no card. Free covers one live-app pentest, one repo scan, uptime monitoring, a basic WAF and MCP tools. Pentest-Tools.com is a good hosted scanner toolbox. Compare total coverage, not just the scan line, since Jikida also blocks attacks and watches uptime. See /features.
Yes. Jikida runs a live-app pentest (DAST) against the running site. It checks security headers, TLS, exposed .env and .git files, open ports, admin panels, CORS, reflected XSS, subdomain takeover and GraphQL introspection. Each finding gets a fix, and the whole result is graded. It runs on a schedule, not just on demand.
It adds the parts a scanner toolbox does not have. Jikida scans your repo for secrets and vulnerable dependencies, blocks live attacks with a managed WAF, and monitors uptime, SSL and domain expiry with a phone alarm. It also runs the pentest on a schedule and grades it, so you do not start each scan by hand.
Yes, no card needed. Free covers one live-app pentest, one repo scan, uptime monitoring, a basic WAF and MCP tools for AI IDEs. Paid plans add scheduled deep pentests, monthly repo scans, the full managed WAF and unlimited MCP scans.
Yes. The Jikida CLI runs with npx @jikida/scan and outputs SARIF, so results show up in your code host. Use --fail-on to fail a build on findings at or above a severity you set. You can run it in CI beside any on-demand scanner you already use, with nothing to migrate.
One platform · One install
Pentest, scan and protect from one account.
A live-app pentest, repo and secret scanning, a managed firewall and monitoring — free to start, no card. Plans from $15/mo.